Articles
What Does Good GRC Look Like for a Regulated Financial Services Firm?
Most firms don’t lack governance.They lack unified visibility - the kind that shows what’s working, what’s not, and what’s changing in real time In today’s…
Connect obligations, risks, policies, controls and evidence in one place, so you can show not just that you're compliant, but how, when and by whom. Built for regulated financial services firms.
70%
faster audit preparation
100%
evidenced task audit trail
75%
reduction in attestation workflow time
Obligations, policies, controls and evidence often sit across separate systems and teams, making ownership harder to trace and assurance more difficult to demonstrate.
Regulatory obligations are often tracked separately from the policies, controls and actions intended to address them. This makes it harder to see what changed, who owns the response and what remains outstanding.
Policies live in shared drives, while controls, tasks and attestations are managed through email and disconnected tools. This makes it difficult to prove that policy has been translated into action. Policy sets the direction; a well-run control framework, aligned with it, delivers the intended outcome.
Evidence is often gathered manually when an auditor, client or regulator requests proof. Teams must reconstruct historical activity from inboxes, spreadsheets and documents rather than retrieve it from a single, immutable source.
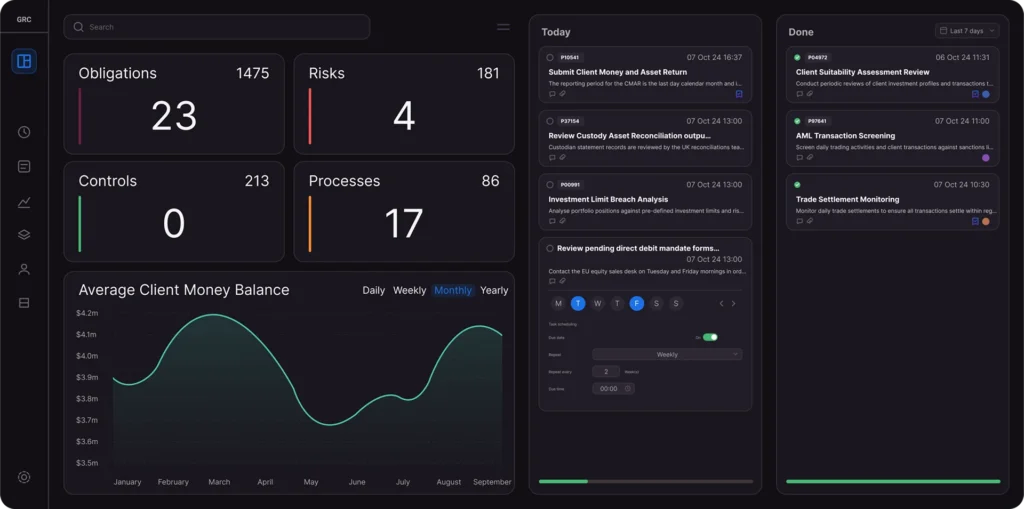
GRC brings obligations, policies, controls, risks, actions, attestations, incidents and evidence into one connected environment for regulated firms. It links governance activity to accountable owners and retained evidence, helping teams manage oversight as business-as-usual work rather than rebuilding the record whenever scrutiny arises.
Connect requirements to accountable owners, completed actions and retained evidence, giving teams stronger oversight and proof when scrutiny arises.
Bring regulatory obligations together with the policies, controls and actions that respond to them. Each requirement is traced from source to owner, so when something changes, accountability is clear and nothing falls through the cracks.
Bring risk registers, monitoring and control activity into one connected view, with evidence recorded automatically as work is completed. Teams spot issues before they escalate and can answer any audit or regulatory request immediately from a single, trusted source, with no chasing through inboxes or spreadsheets.
Policies stop sitting in shared drives. Each one connects to the controls, tasks and attestations that put it into practice, and to the incidents, breaches and remediation that arise when it’s tested. Teams get a single, auditable trail from requirement to resolution.
Link incidents, breaches, complaints, failed controls and risk events to accountable owners and remediation activity. This gives teams a more complete view of issues from identification through to resolution and closure.
This is where AutoRek comes in
Bring obligations, policies, risks, controls and evidence into one environment, giving teams clearer ownership, stronger oversight and proof on demand.
Tracks obligations from regulatory sources, highlights changes and supports mapping to affected policies and controls.
Apply GRC to the obligations, controls and assurance priorities that matter most across payments, asset management and capital markets, and banking.
Connect obligations, policies, risk, CASS controls and assurance in one record, with clearer ownership and evidence of completed actions.
Connect regulatory change, risk, policies, controls and incidents, with clearer ownership, remediation tracking and ongoing assurance.
Connect safeguarding obligations, controls, attestations and incidents, with clear ownership, tracked actions and evidence in regulated operations.
Research, guides and updates on the operational and regulatory challenges facing regulated firms.
Articles
Most firms don’t lack governance.They lack unified visibility - the kind that shows what’s working, what’s not, and what’s changing in real time In today’s…
Articles
Modern-day financial regulation is moving faster than spreadsheets. The pace and volume of regulatory change show no signs of easing. From Consumer Duty to evolving…
Articles
GRC programs are meant to create confidence. Yet for many regulated firms, it feels more like a burden. Spreadsheets, manual sign-offs, disconnected tools, and duplicated…
Clear answers to the key questions regulated firms ask when evaluating GRC software for obligations, policies, controls, risks, evidence and audit readiness.
GRC software brings governance, risk and compliance work into one system: the obligations you must meet, the risks and controls that address them, who owns each one, and the evidence that it was done.
Compliance, risk, client asset, internal audit, operations and HR teams in regulated financial services firms, from the senior managers who need oversight to the people completing actions and attestations.
GRC is positioned as an actively applied controlled policy library in which policies can be linked to the controls that deliver them and supported by traceable sign-offs and attestations.
Completed tasks and attestations are captured as evidence through business-as-usual governance activity, helping audit readiness become an ongoing business activity rather than a separate evidence-gathering project.
GRC enables teams to log incidents, breaches and complaints, link them to relevant controls or risk events, track remediation, and maintain clear reporting from identification through to resolution.
GRC connects obligations, risks, policies, controls, actions and evidence, giving regulated teams clearer ownership, continuous oversight and proof when it is needed.